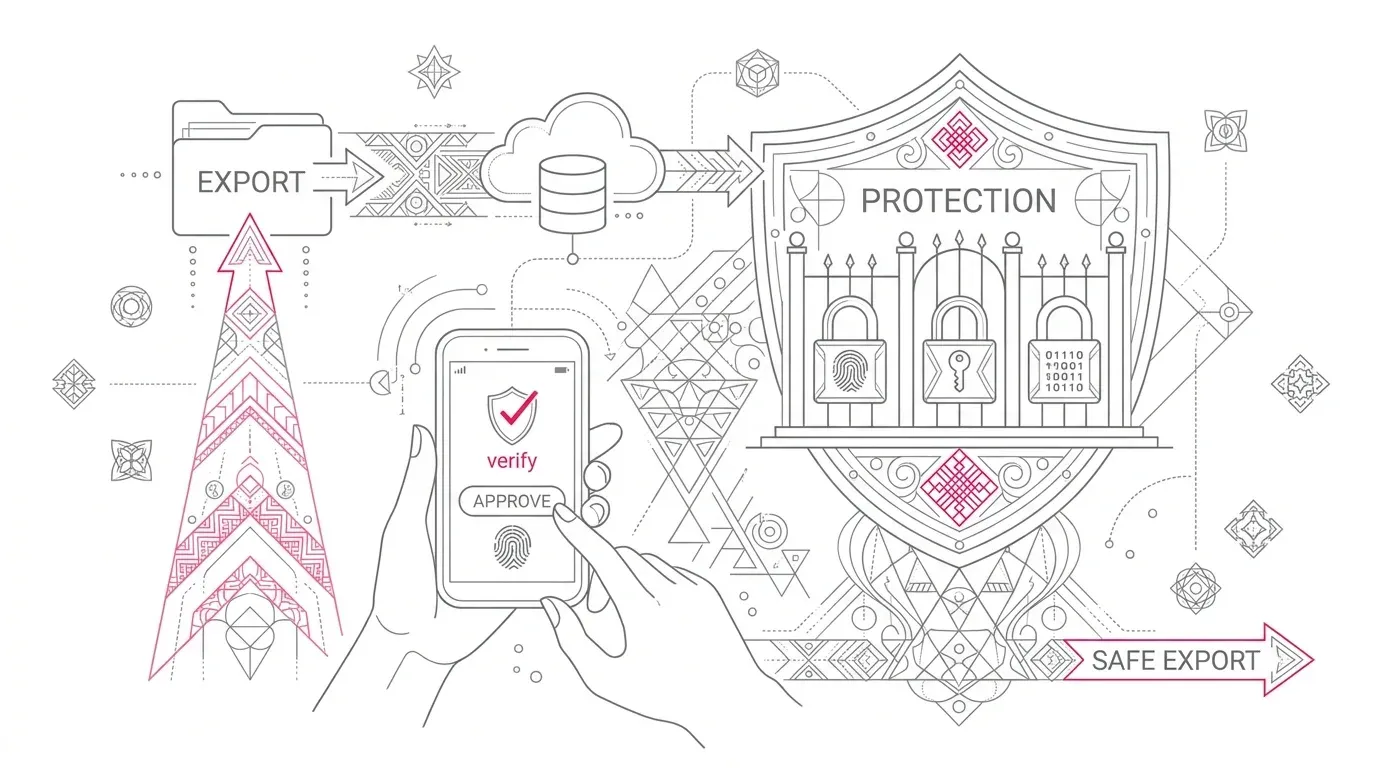
Your users can sign in through SSO, open a Salesforce report, and still be asked to verify their identity when they click Export. That is expected behavior under Salesforce's report step-up authentication control , not proof that SSO failed.
The difficult part is what happens next. Some users do not have a Salesforce verification method ready. Others hit passkey or browser problems. Spreadsheet connectors can behave differently from the Salesforce UI. A workflow that quietly depended on one employee downloading a report and emailing it every morning can suddenly become a support queue.
Salesforce introduced the control because report exports can move a large amount of data out of the platform in one action. The right response is to preserve that protection while removing avoidable manual exports and fixing the workflows that remain.
What Salesforce report step-up authentication actually does
Salesforce's current guidance says the mandatory policy applies to interactive report export and print actions in paid production and sandbox orgs. It does not apply merely because a user views a report or dashboard.
The distinction between login and step-up matters. A user can complete MFA at an external identity provider, establish a valid Salesforce session, and later receive another challenge at export time. Salesforce treats the export as a higher-risk action and requires a fresh assurance check when the configured step-up period has expired.
Admins can set the period from 1 to 120 minutes. The setting changes how often an eligible user may be challenged; it does not remove the control. Salesforce also says the action fails closed. If verification fails or the MFA service is unavailable, the export is blocked.
For federated SSO users who do not have a Salesforce-native verification method registered, Salesforce can fall back to email or SMS one-time passcodes. That makes current contact data, verifier enrollment, and user instructions part of reporting availability.
Salesforce documents an alternate treatment for tightly controlled network sessions. A user may avoid the step-up prompt when profile login IP restrictions are configured and the request meets Salesforce's stated conditions. Do not apply broad IP restrictions simply to suppress prompts. Evaluate the control with your identity and security owners, especially for remote work, managed devices, multiple locations, and incident recovery.
First, classify the reporting workflow
Many organizations treat every report download as the same technical action. It is more useful to classify the business job before changing a setting.
One-off analysis
An analyst downloads a filtered report to investigate a service backlog, reconcile a campaign, or answer an audit question. The export is initiated by a person and may contain sensitive detail.
Keep step-up authentication in the path. Make the challenge reliable, train the affected users, and confirm that the export matches the report they reviewed.
Recurring internal distribution
A service manager exports the same case report every Monday and emails it to a fixed internal list. The manual click adds little control. It adds delay, inconsistency, and a person-dependent failure point.
Assess a native Salesforce report subscription or another governed scheduling pattern. Salesforce says scheduled and subscribed reports run in a background context and are not subject to the interactive step-up challenge. The resulting delivery still needs an approved running user, shared report folder, verified sending identity, appropriate recipients, and monitoring. Review the current subscription instructions before redesigning the workflow.
Recurring external distribution
A foundation sends grant-status reports to program partners. An insurer sends operational reports to brokers or vendors. A healthcare organization shares approved information with an external service provider.
This is not simply an authentication problem. It is a data-release process. Define the recipient, purpose, minimum necessary fields, frequency, retention expectation, delivery method, and owner. Native subscriptions have licensing and recipient constraints. An AppExchange product may add useful delivery options, but it must be assessed against the same access, privacy, and operational requirements.
Spreadsheet and connector retrieval
A workbook, Google Sheet, or desktop tool refreshes from a Salesforce report. Some connectors use report export endpoints; others use an API. Salesforce exempts non-interactive API sessions from report step-up authentication, but that does not mean every connector is unaffected or that API access is a security exception.
Identify the connector, authentication flow, endpoint, running identity, data scope, refresh behavior, storage location, and failure handling. Test the current supported version. Do not assume that a manual-export workaround, copied session, or unsupported URL will remain reliable.
Why SSO users still get challenged
SSO answers whether the user can establish a Salesforce session. Step-up authentication answers whether the person taking a sensitive action can provide the assurance Salesforce requires at that moment.
This is why "our users already have MFA" is not enough to diagnose the problem. Ask four specific questions:
- Which method did the identity provider use, and what assurance signals reached Salesforce?
- Does the user have a supported Salesforce verification method registered?
- Can the user receive the fallback email or SMS code at the address or number on record?
- Does the challenge complete correctly in the supported browsers and device configurations the organization actually uses?
Build the support script around observable evidence. Record the user type, browser, verification method, report format, row count, timestamp, error, and whether the same action succeeds in another supported context. Check Salesforce Trust and Known Issues before changing controls.
A seven-step remediation plan
Step 1: Inventory manual report exports
Start with people and business processes, not only configuration. Interview report-heavy teams and review help-desk tickets, report ownership, subscriptions, connected apps, and scheduled jobs. Capture:
- report name and owner;
- business purpose and decision supported;
- user population and frequency;
- internal or external recipients;
- data classification and sensitive fields;
- format, size, row count, and destination;
- current identity and authentication path;
- downstream spreadsheet, upload, or reconciliation steps;
- business owner and technical owner.
The inventory will usually reveal recurring exports that should not depend on a person clicking a button.
Step 2: Set the session policy deliberately
Confirm that Reports and Dashboards uses the export-and-print policy rather than a broader legacy selection that causes more prompts than intended. Choose the step-up period within Salesforce's 1-120 minute range based on risk and actual work patterns.
Document any use of profile IP restrictions as an alternate measure. Test remote access, VPN transitions, office networks, and session changes. A control that only works under ideal network conditions will create exceptions during the moments when teams most need reports.
Step 3: Prepare every affected user
Find the internal users who export reports, including Chatter Plus users and employees who enter through an Experience Cloud site. Salesforce says external Experience Cloud users are exempt, but internal users accessing reports through an Experience Cloud site can be blocked and may need to use the internal org.
For each affected user, verify:
- an approved Salesforce verification method is enrolled or a valid fallback channel exists;
- the device and browser support the selected method;
- the user knows that SSO login does not eliminate the export challenge;
- the support team has a recovery procedure that does not ask users to share codes or credentials.
Printing or exporting a report during a Partner Contact Center call can trigger step-up authentication and disconnect the call, according to Salesforce's current Help article. Include that scenario in agent guidance where it applies.
Step 4: Test complete report workflows
Do not stop when the verification screen disappears. Test the business outcome.
Use representative personas, reports, formats, browsers, and data volumes. Confirm that:
- the intended report version and filters are used;
- the correct file downloads once;
- the format opens successfully;
- row counts and totals reconcile to Salesforce;
- restricted fields remain absent;
- large exports behave as expected;
- users can recover from cancellation, timeout, or a failed challenge;
- help-desk staff can reproduce the problem without needing the end user's verifier.
Salesforce has documented defects during the rollout, including issues involving Login As , embedded dashboards, large exports , and duplicate downloads . Check each Known Issue's current status and affected release before using it as the diagnosis for a new case.
Step 5: Replace repetitive downloads with governed delivery
Native report subscriptions should be the first comparison point. They can deliver refreshed results on a schedule and are exempt from the interactive step-up flow, but they are not unlimited. Salesforce documents per-user subscription caps, recipient requirements, and attachment limits , including limits on rows, columns, and file size.
Where native subscriptions do not meet the need, evaluate a supported reporting application. Yuniq's current AppExchange listing describes Report & Dashboard Scheduler as a native Salesforce application that can schedule Excel and PDF outputs for internal and external recipients. Its stated capabilities may fit teams that repeatedly export, format, and email reports.
Treat this as a product evaluation, not a security workaround. In a sandbox, validate the package version, permissions, running-user model, recipient controls, report fidelity, volume limits, email deliverability, logging, failure alerts, and compatibility with step-up authentication. Confirm contract, data-processing, and regulatory requirements with the appropriate reviewers.
Step 6: Govern API and connector access separately
Salesforce says non-interactive API report access is exempt from the step-up requirement. An API path can be appropriate for a managed integration, but it should not become an unowned route around an interactive control.
Require a named owner, least-privilege identity, supported OAuth flow, restricted data scope, credential lifecycle, monitoring, error handling, and reconciliation. Confirm where retrieved data is stored and who can open it after it leaves Salesforce. For spreadsheet connectors, test refresh failure, revoked access, user departure, and changes to report structure.
Step 7: Monitor the business outcome
Track more than successful challenges. Measure blocked exports, support tickets, repeated manual downloads, failed scheduled deliveries, stale recipient lists, reconciliation errors, and sensitive reports with no current business owner.
Review the workflow again after a full reporting cycle. A working export is not proof that the right data reached the right person, or that the organization can explain why the distribution still exists.
Industry-specific implications
Healthcare
Patient, member, provider, case, and service reports can contain regulated or highly sensitive data. Step-up authentication reduces the chance that a hijacked interactive session can immediately export a report, but it does not decide whether the report contains the minimum necessary information or whether the destination is appropriate.
Review field selection, running-user access, recipient authorization, secure delivery, retention, and downstream copies. Ask qualified privacy and security reviewers to assess applicable obligations. Do not treat Salesforce configuration as a compliance conclusion.
Insurance
Claims, policy, underwriting, broker, and service reports often move on fixed operational cycles. Manual exports create concentration risk around individual employees and can fail at month-end or during incident response.
Classify which outputs are ad hoc decisions and which are controlled data products. Automate the latter only after reconciling totals, recipient scope, and exception handling across a full business cycle.
Nonprofit foundations
Lean teams may rely on a small number of Salesforce power users to prepare donor, grant, board, and program reports. An export challenge can expose that person dependency. External recipients may also fall outside what a native subscription can serve.
Prioritize the reports that support funding decisions, grant oversight, and board deadlines. Remove unnecessary fields, document the running user, and select a delivery pattern that remains supportable when the usual administrator is unavailable. Yuniq's AppExchange listing currently states that nonprofit discounts are available; confirm current pricing and eligibility directly before publication or purchase.
What not to do
- Do not disable or weaken a security policy simply because users were surprised by it.
- Do not assume SSO login proves that Salesforce can complete the export-time challenge.
- Do not turn an API or spreadsheet connector into an unowned bypass.
- Do not automate distribution before verifying the running user's access and recipient list.
- Do not use a Known Issue as the diagnosis without matching the current status, release, symptoms, and reproduction conditions.
- Do not equate a delivered file with correct, complete, or authorized data.
A practical decision rule
Keep step-up authentication for interactive, human-initiated exports. Fix enrollment and support where those exports are justified. Move stable, recurring distribution into a governed subscription, integration, or scheduling product that has been tested for identity, access, data accuracy, delivery, and recovery.
If report-export MFA has become a daily operational problem, Yuniq's Salesforce services team can help map the reporting and identity workflow. For recurring delivery requirements that exceed native subscriptions, evaluate Yuniq Report & Dashboard Scheduler in a sandbox against your security, recipient, volume, and reconciliation requirements.